 Vijay Singh
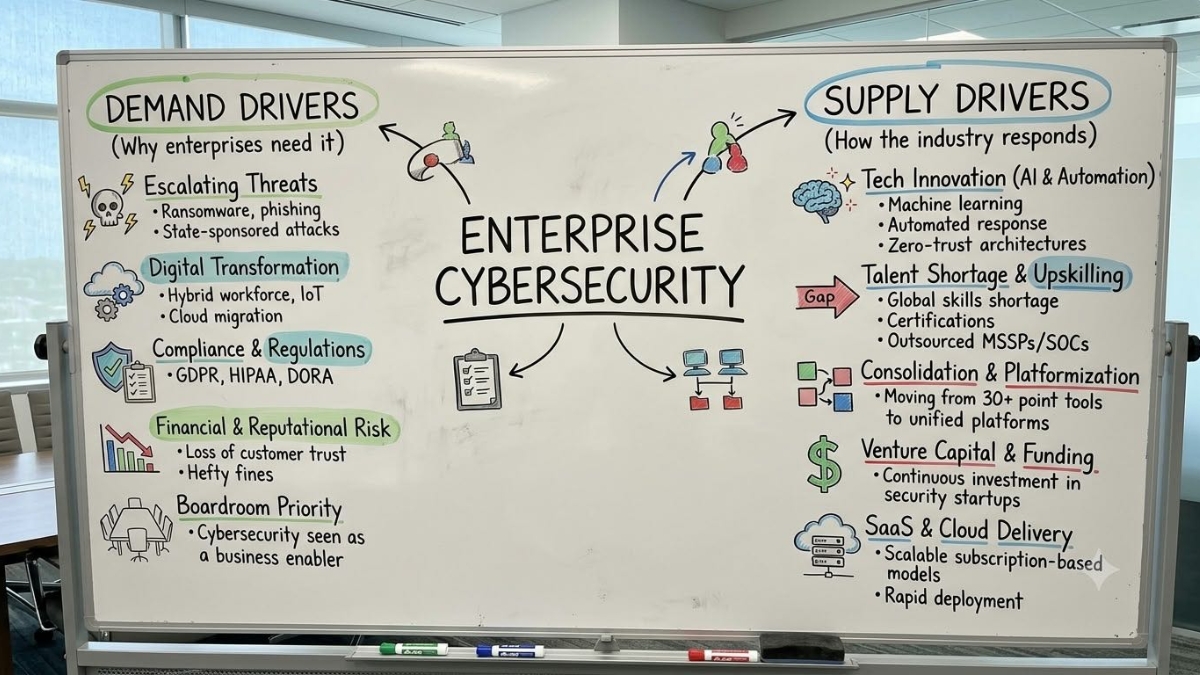
Where enterprise security leaders are investing this quarter — and whether the specialized cybersecurity talent to deliver it actually exists right now.
New Delhi [India], October 12: The number one security priority this quarter represents the acute bottleneck in enterprise hiring: high strategic focus paired with scarce experienced bench depth. While enterprise technology leaders are converging on the same three defensive priorities, the market reality shows severe talent demand supply friction across implementation partners and internal teams alike.
PART ONE: DEMAND — Analyzing Cybersecurity CISO Intent Across 100+ Enterprise Leaders
Based on proprietary cybersecurity talent intelligence drawn from direct consultations with sitting CISOs, security directors, and technology heads across banking, manufacturing, energy, and digital services (Q3–Q4 2026).
Priority 1: Endpoint Detection and Response — 61% Named It Top Three
This marks the highest single-category concentration in our talent demand supply index to date. The underlying driver is not a novel exploit family, but a fundamental realignment in attack vectors.
The Sophos State of Ransomware 2026 report, surveying 2,158 organizations across 17 countries, established that ransomware delivery mechanics have altered significantly. Email-borne attacks (26%) and weaponized phishing campaigns (24%) have officially outpaced software vulnerabilities (18%) as primary initial access vectors — reversing a multi-year trajectory.
Strategic takeaway: Endpoint security is no longer merely a device-management exercise; it is an identity, human, and communication-channel problem. Enterprise leaders procuring endpoint tooling must recognize that the underlying challenge requires unified telemetry. CISOs addressing this proactively are coupling endpoint and identity architectures together, heading off the budget bloat and integration delays of two distinct procurement cycles.
Priority 2: Identity and Access Management — 54%, Rapid Acceleration
IAM has transitioned from an IT operations ticket item into an urgent cybersecurity CISO intent signal. The empirical catalyst: research reveals that in 97% of ransomware incidents where credential compromise served as the root cause, multi-factor authentication was operational somewhere within the target environment.
Strategic takeaway: Having MFA operational somewhere is fundamentally distinct from achieving complete enterprise surface coverage. The primary deficit is not tool licensing — it is architectural coverage mapping. Most organizations cannot pinpoint which legacy endpoints, internal APIs, and service accounts remain unprotected. The requirement is not simple MFA rollout; it is comprehensive gap remediation, requiring specialized cybersecurity talent to audit and bridge identity silos.
“The board asked whether MFA was enabled, and the operational checklist said yes. Nobody probed where it remained absent across legacy architectures. That blind spot proved to be the exact vulnerability vector.”
— CISO, Tier-2 Financial Institution
Priority 3: Cloud Security Posture Management — 46%, Steady Intent
Demand remains consistent, though near-term execution is deferring to contract cadences. CISOs indicate execution schedules will align with Q1/Q2 annual enterprise cloud renewals. This positioning makes cloud security posture the rare domain where strategic demand remains elevated, yet near-term implementation urgency remains calm.
Priority 4: Security Operations Automation — 39%, Transitioning from Planning to Execution
The percentage contraction from 52% in prior cycles reflects healthy maturity rather than deprioritization. Projects initiated in earlier quarters have shifted from strategic roadmaps into operational engineering — signaling an established category absorbing steady capacity.
Priority 5: OT and Industrial Control Security — 25%, Mandate-Driven Surge
Cybersecurity CISO intent across industrial and utility operations is largely anchored in compliance obligations, driven by mandates like the CEA Cyber Security in Power Sector Regulations 2026. Non-power critical infrastructure operators are closely auditing their programs as cross-sector compliance mandates expand.
“The regulatory deadline triggered a simultaneous market rush. Because organizations approached the same tier of OT systems integrators, premium deployment capacity was exhausted almost immediately.”
— VP of Infrastructure Security, Regional Power Provider
PART TWO: SUPPLY — Mapping Cybersecurity Talent Availability Across Integrators
Continuous cybersecurity talent intelligence derived from ongoing assessments of 68 managed security services providers (MSSPs), systems integrators, and elite advisory firms tracking real-time bench availability, engineering capacity, and project allocations.
The Core Finding: Diverging Talent Demand Supply Curves
In the two domains dominating cybersecurity CISO intent — endpoint detection and IAM — experienced, unallocated cybersecurity talent has reached annual lows. Conversely, segments with available engineering capacity, such as cloud security reviews, are being deferred by buyers until upcoming quarters.
| Domain | CISO Intent Rank | Market Talent Availability |
| Endpoint Detection & Response | #1 (61%) | Severely Constrained |
| Identity & Access Management (IAM) | #2 (54%) | Critical Bottleneck |
| Cloud Security Posture (CSPM) | #3 (46%) | High Availability (Q4) |
| SecOps Automation (SOAR) | #4 (39%) | Maturing / Moderate |
| OT & Industrial Security | #5 (25%) | Fully Booked (Regulation) |
Endpoint Detection & Response | #1 (61%) | Severely Constrained |
Identity & Access Management (IAM) | #2 (54%) | Critical Bottleneck |
Cloud Security Posture (CSPM) | #3 (46%) | High Availability (Q4) |
SecOps Automation (SOAR) | #4 (39%) | Maturing / Moderate |
OT & Industrial Security | #5 (25%) | Fully Booked (Regulation) |
Endpoint Detection and Response: Broad Offerings, Narrow Sector Experience
Across 68 tracked integration practices, 41 maintain deployment teams capable of mobilising within 4–6 weeks. However, only 14 possess referenceable track records delivering within heavily regulated financial services or healthcare perimeters. Navigating stringent compliance constraints, data residency mandates, and enterprise SOC handoffs routinely adds 3–4 weeks to project lead times when teams encounter them without sector experience.
Talent intelligence insight: Procurement vetting must look beyond high-level capabilities to verify named engineering personnel who have executed within the specific regulatory sector.
Identity and Access Management: The Capacity Bottleneck
Among the 68 tracked firms, 29 have zero uncommitted IAM delivery capacity through Q2 2027. The remaining 39 operate with fragmented allocation, leaving lead architects stretched thin across concurrent engagements.
Talent intelligence insight: The speed of IAM adoption has outpaced the pipeline of seasoned engineers. Practices that maintained modest specialist teams have seen market requests double without an equivalent influx of qualified practitioners. Enterprises engaging IAM projects must ensure their provider provides experienced architects rather than generalist security engineers learning identity controls on site.
“Our integrator committed to an early start date, but that only covered administrative onboarding. The actual identity architects were tied up on another enterprise migration for ninety days. That lag was never surfaced during the RFP.”
— Head of Identity & Access, Multinational Banking Group
OT and Industrial Security: Compliance Absorbency
Across 42 tracked practices with dedicated operational technology security groups, deployable bench capacity dropped by 38% between July and October 2026. Twelve firms with unallocated personnel in Q3 are committed into late 2027.
Talent intelligence insight: Hard compliance deadlines and enforcement clauses naturally capture top-tier engineering talent. Unregulated or voluntary security modernization initiatives risk being staffed with secondary benches unless access to proven specialists is secured early.
Cloud Security Posture: The Contrarian Sourcing Window
Fifty-four of the 68 monitored providers currently report open availability across their cloud posture and architecture practices. With general enterprise demand slated for procurement cycles in early 2027, Q4 presents an opportune buyer’s window.
Talent intelligence insight: Initiating cloud security posture reviews while broader enterprise demand is low enables buyers to secure premier architectural teams ahead of the Q1–Q2 annual renewal rush.
Security Operations Automation: Experienced Capacity Coming to Market
As multi-year SOAR and automation rollouts wrap up, delivery practices that expanded through 2024–2025 are seeing seasoned engineers return to the bench. Organizations entering the automation market now can tap practitioners with battle-tested deployment experience rather than theoretical tool certifications.
Talent Intelligence: Market Realities for Enterprise Leaders
- Deployment Lead Times: Across tier-one service providers, the window between contract signature and actual deployment of named, senior engineering talent averages 6–9 weeks.
- Regulatory Prioritization: Compliance-mandated deadlines consistently monopolize premier engineering teams across providers, leaving discretionary modernization projects to navigate thinner bench depth.
- Boutique Availability vs. Large Integrator Backlogs: Mid-market and specialized boutique security firms currently reflect higher proportions of uncommitted senior talent across core domains compared to global multi-practice integrators whose teams remain tied up in long-term programs.
Methodology
- Cybersecurity CISO Intent Data: Sourced via structured qualitative interviews and quarterly surveys with 100+ cybersecurity decision-makers (CISOs, CIOs, and SVPs of Security) across banking, energy, manufacturing, and tech services (Q3–Q4 2026).
- Cybersecurity Talent Intelligence & Supply Data: Continuous capacity tracking across 68 systems integrators, MSSPs, and boutique security consulting firms evaluating bench utilization, domain certifications, active allocations, and projected roll-offs.
- Referenced Research: Sophos State of Ransomware 2026; Central Electricity Authority (CEA) Cyber Security in Power Sector Regulations 2026.
About Analyst Layer
Analyst Layer delivers actionable talent intelligence and enterprise technology advisory, tracking real-world talent demand supply metrics through continuous engagement with enterprise executives and global delivery ecosystems. Operating in affiliation with IIT Bombay TIH, Analyst Layer bridges strategic technology roadmaps with actual delivery market capacity.
Inquiries regarding sector talent availability, customized benchmarking, or executive roundtables: contact index@analystlayer.com.